SSO, SyteLine roles, your choice of deployment and SOC 2 Type II compliant infrastructure. Written for the IT or ERP manager who approves the project.
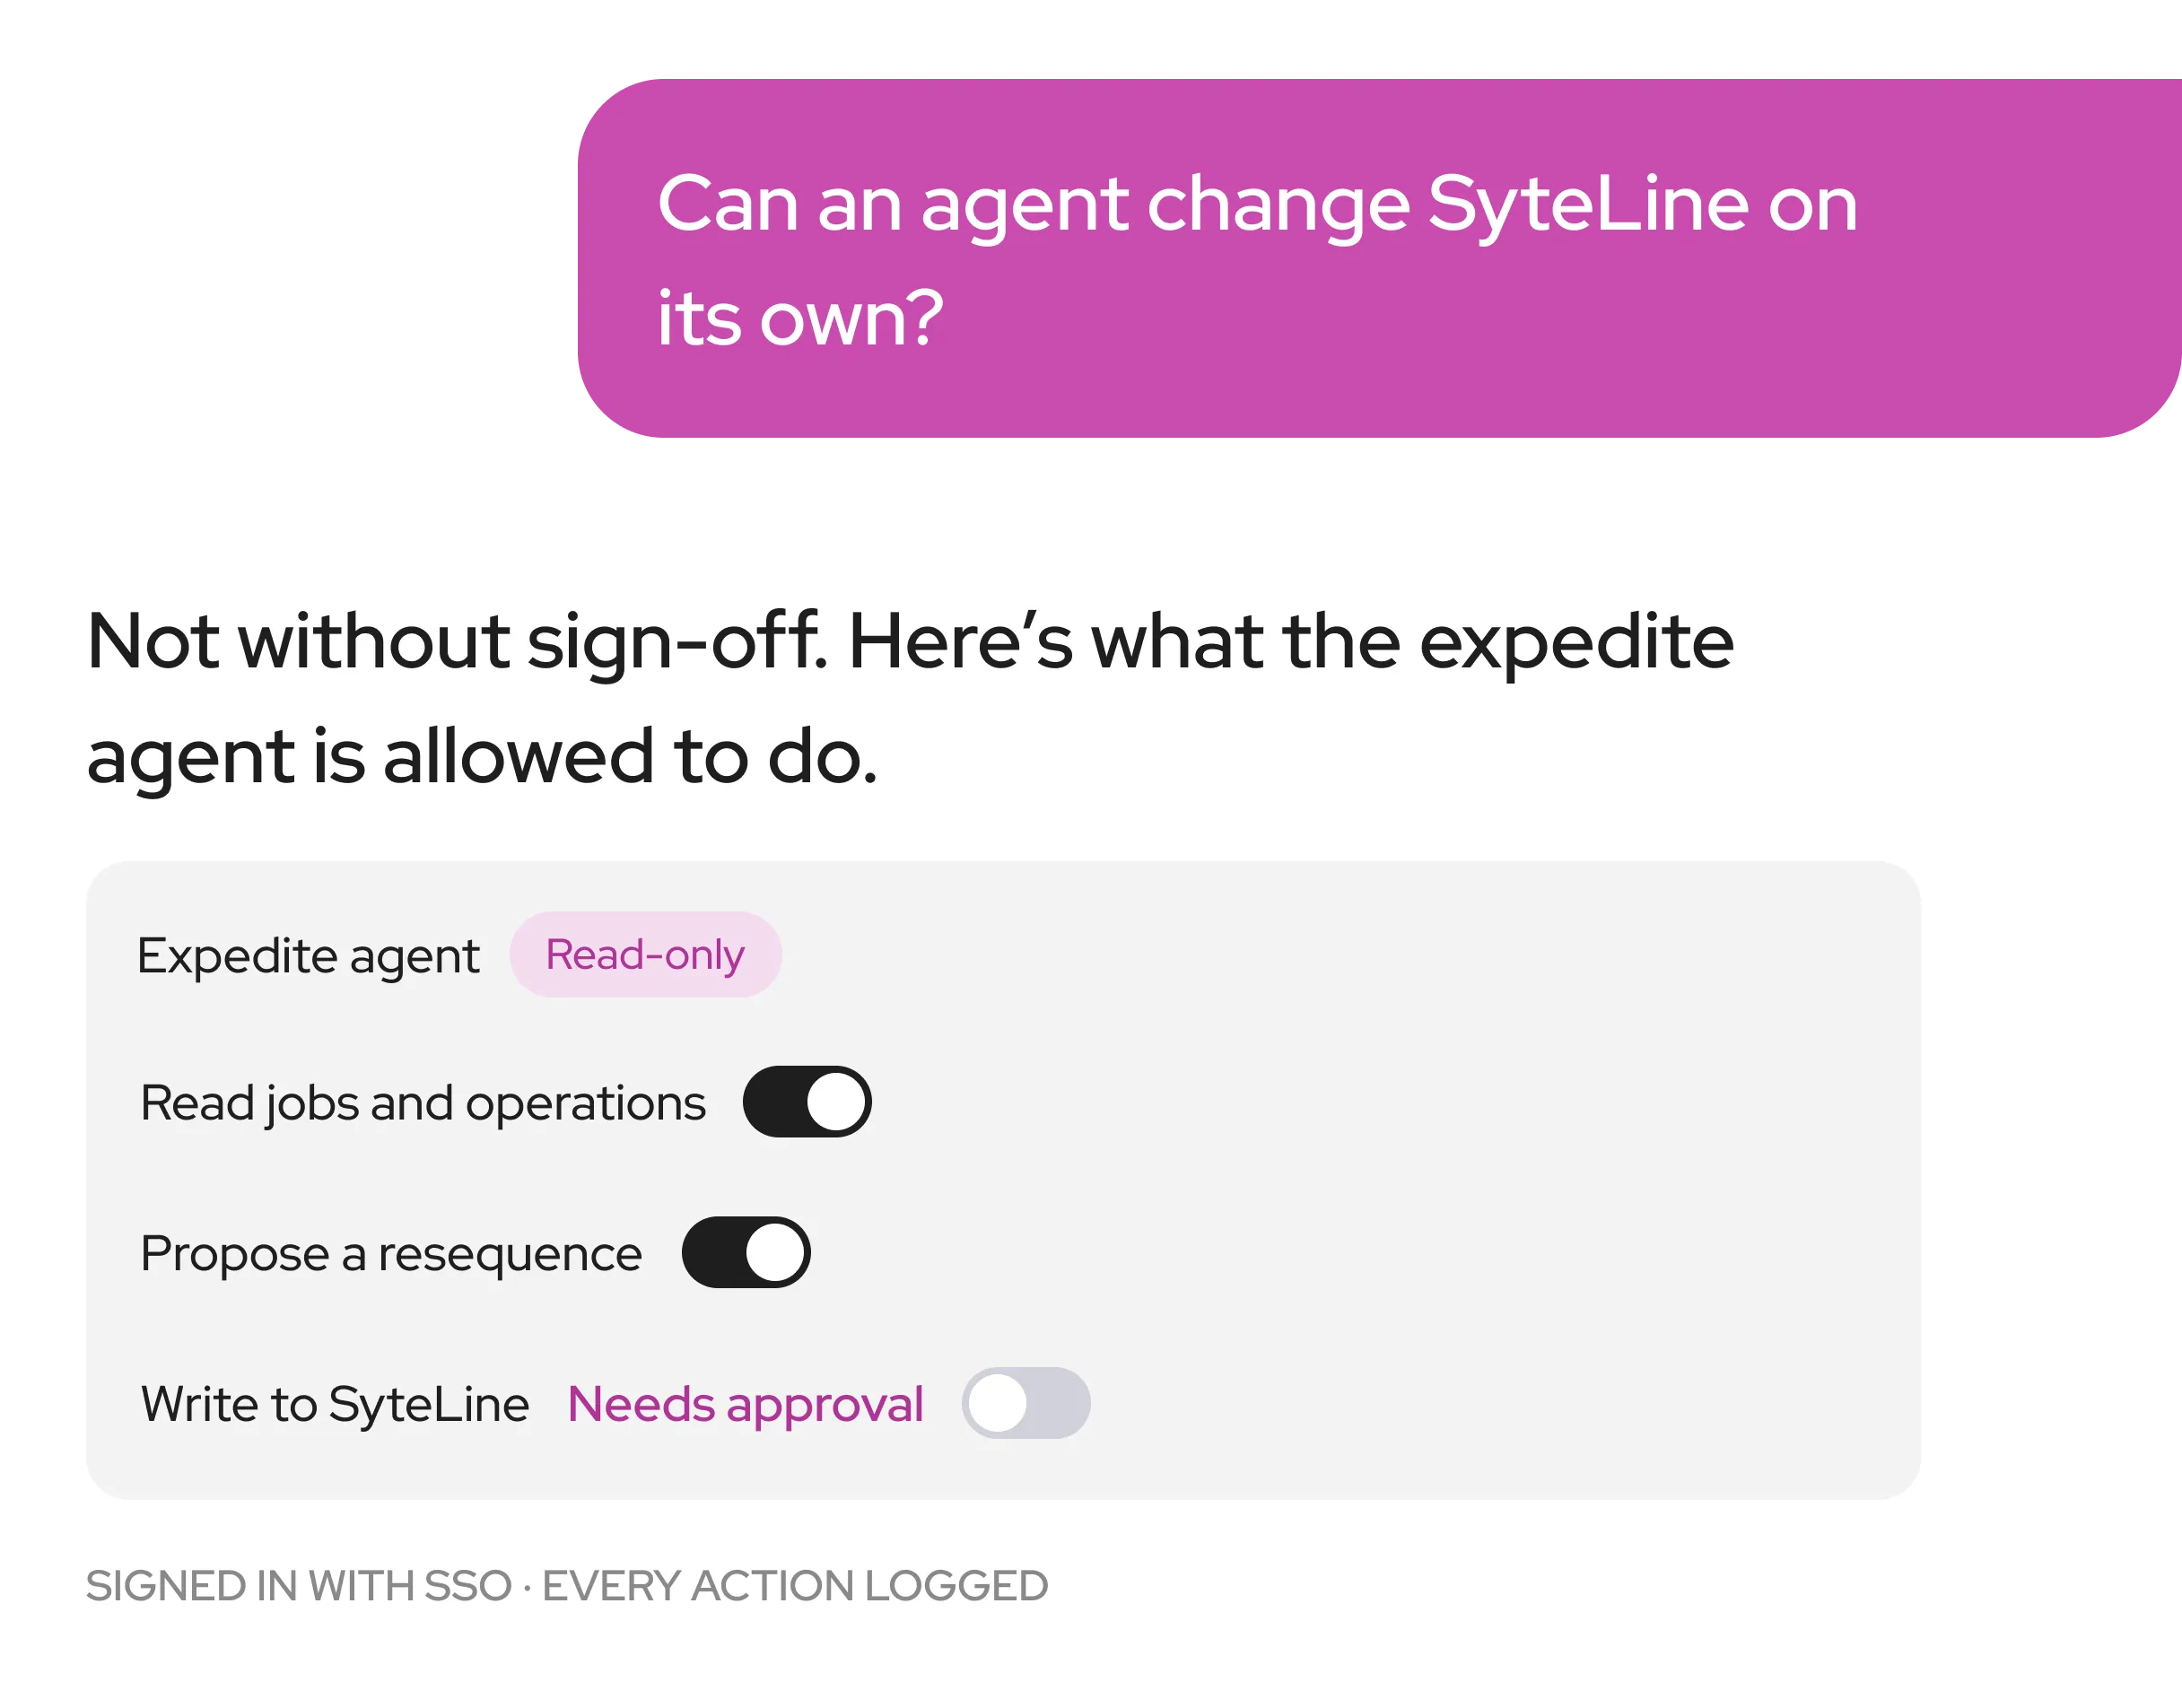
Permissions are enforced when an answer is retrieved, not written into a prompt. When someone leaves and you switch off their account, their access to the AI goes with it.

On-prem, in your own AWS or Azure account, or a dedicated environment we manage. You can change your mind later.
Agents start read-only, run in your test environment first, and you decide which actions need a person’s sign-off.

People sign in with the identity provider you already use. No new passwords, no shared logins.

Each connector gets only what its workflow needs: specific IDOs, one named mailbox, one document folder.

You set how long questions, answers and logs are kept. Export them any time.
Any agent can be paused without affecting SyteLine or the rest of the layer. Approvals and before-and-after values are logged.
Your ERP team will care most about agents that can change SyteLine. Every agent follows the same rules.
A new agent can look and propose. It cannot change anything.
Every write workflow runs against your SyteLine test environment before it touches production.
You decide which actions need sign-off. The approval and the before-and-after values are logged.
Four kinds of AI reach a SyteLine shop. When each fits, what you should own, and ten questions to ask.
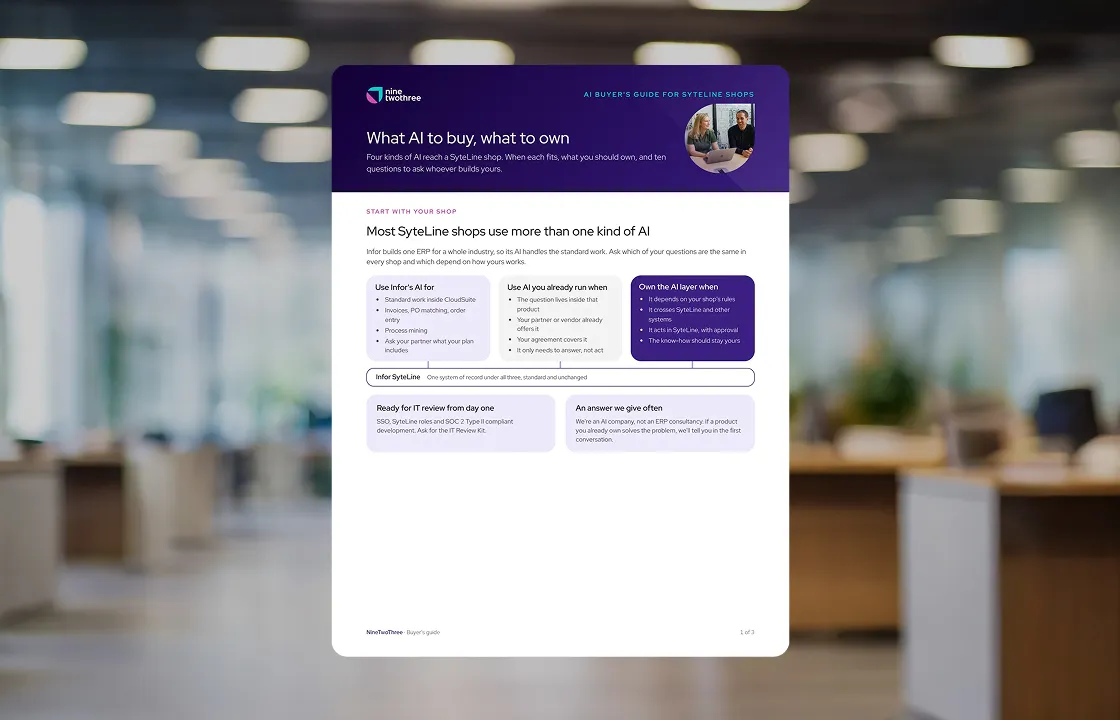
Where Infor’s AI fits, when a tool you already run is enough, and when the AI layer should be yours.
What a personal chatbot account can’t do: know your rules, act in SyteLine, or keep your data where you choose.
Your rules, the code and prompts, the record of what the AI did, model choice, training rights and an exit.
Price, people, SyteLine roles, data, scale, upkeep and ownership, and how NineTwoThree answers each.
Not in cloud SyteLine, where Infor doesn’t allow it. We use the ION API Gateway, Mongoose IDOs and the Data Lake. On-prem, we prefer a read replica or IDO calls over direct writes to the database.
Reads are scheduled and cached for each view, and agents call the same APIs your integrations already use. We agree load limits with your ERP team during validation.
A test-environment login with a scoped role, an SSO app registration, and an hour with whoever owns SyteLine security.
Your data and logs stay inside the boundary you choose: on-prem, your own cloud account, or a dedicated environment. People sign in with your SSO and see only what their SyteLine role allows. Every read and write goes through a governed gateway, agents start read-only, and every action is logged. The infrastructure is SOC 2 Type II compliant, and models run under terms that exclude training on your data.
We change nothing inside the SyteLine core, so there’s nothing to re-apply after an upgrade. Cloud SyteLine updates monthly, and we test the layer’s connections against each release in your test environment before it reaches you.
On-prem, single-tenant and CloudSuite.
Code, prompts and the Shop Map sit in your repo.
60 days of Align and Validate at a fixed price.
Your senior people’s rules stay in the company.
See a late order while there’s still time to move it.
What changed on your orders overnight, before the shift.
You decide which actions need a person’s sign-off.
Book an hour with our engineers and bring your security questions, or start with a 45-minute Shop Walk on one real workflow.
Meet with founders Andrew Amann & Pavel Kirillov

Custom AI implementation roadmap
No sales pressure


